Security Halloween: Backdoored AI Extension, $6.3B Crypto Heist, and a Day of Authorization Failures
On Halloween 2026, Hacker News surfaced what may be the most alarming single-day cluster of security disclosures in recent memory — a backdoored VS Code extension, a $6.3 billion exchange hack executed in twenty minutes, two platform breaches, and five distinct cloud tenant isolation failures. The rest of the day's feed mixed retro computing triumphs, AI-assisted engineering debates, and glacier archaeology into an unusually rich Saturday.
“The archaeology, as the piece notes, is racing the climate.”
How this was made Verified AI
Every Intellegix briefing is generated from that day's broadcast and run through automated checks before it publishes — with a human paged on any flag. Here is the trail for this edition.
Five Ways the Walls Failed: A Security Catastrophe in One Day's Feed
The day's most-discussed story — 908 points and 533 comments as of the podcast's scrape — was a disclosure from a firm called Phorion about a backdoored extension on the Cursor marketplace presenting itself as the official Claude Code extension for VS Code. The disclosure appeared at phorion.io under the title 'Official Claude Code VSX Compromise.' VS Code extensions can read the filesystem, access environment variables, execute shell commands, and make arbitrary network calls — placing a malicious extension inches away from AWS credentials, API keys, and dot-env files that developers routinely store inside project directories.
The supply-chain mechanics are what make the attack particularly insidious. Someone built an extension closely resembling Anthropic's legitimate Claude Code offering, listed it on the Cursor marketplace, and waited for installations. The HN thread filled with developers trying to determine whether they had installed the compromised version — and that uncertainty, as much as any confirmed theft, constitutes the harm. Anyone who installed a Claude Code-labeled extension from Cursor's marketplace recently is advised to verify the publisher ID against Anthropic's official documentation, rotate any potentially exposed secrets, and review network logs for unexpected outbound connections. The thread reportedly contains specific indicators of compromise.
Northflank, the developer infrastructure platform used by engineering teams to deploy and manage containerized workloads, confirmed a separate breach that attracted 444 points and 317 comments — a comment count that functions as a rough proxy for how many developers in the community believe they may be personally affected. A third breach, involving Scribd, surfaced not through corporate disclosure but through a community Tell HN post, suggesting the company had not yet gotten ahead of the story. Scribd hosts vast quantities of user-uploaded documents and accounts that often carry payment information.
Operating at a categorically different scale, a Wired report on the Binance hack drew 469 points. Attackers reportedly compromised Binance's internal infrastructure and executed a withdrawal sequence that cleared $6.3 billion in approximately twenty minutes before automated systems flagged the anomaly. Security analysts note that the speed of execution almost certainly reflects weeks or months of quiet pre-positioning — mapping internal systems, understanding authorization flows, and identifying which accounts or keys would need to be compromised before the actual theft began. The regulatory implications of a loss exceeding many sovereign wealth funds' annual returns are expected to trigger renewed scrutiny of exchange custody architecture, key management practices, and detection systems.
Rounding out the day's disclosures, Binary Security published findings of five full cross-tenant compromises in Azure — five distinct root causes, each independently capable of allowing an attacker to move from one Azure tenant into another's resources. Cross-tenant isolation is a fundamental guarantee of cloud hosting; its failure means an attacker who compromises any tenant can potentially reach others sharing the same infrastructure. The research is available at binarysecurity.no, and the HN thread had cloud engineers working through the technical implications. The five root causes are reportedly separate attack paths, meaning patching one does not address the others. The throughline across every disclosure of the day, as observers noted, was an authorization boundary that turned out to be a door rather than a wall.
The Unwinnable Bot War: A Turnstile Solver and an Open-Web Warning
Two stories on Saturday's feed sit in direct and uncomfortable conversation. A GitHub library called cfsolve — posted under the handle chris124567 and drawing 228 points and 66 comments — demonstrates a working solver for Cloudflare's Turnstile CAPTCHA system that requires no headless browser. Cloudflare's Turnstile is designed to be harder to defeat than traditional image-based CAPTCHAs because it performs behavioral analysis and device fingerprinting rather than simply asking users to identify traffic lights. Bypassing it without even launching a browser implies the solver is reverse-engineering Cloudflare's challenge-response mechanism at the protocol level — a technically notable achievement with obvious dual-use implications.
A Tech Policy Press essay appearing the same day argues that the arms race itself is the real problem. The piece contends that aggressive bot-detection measures do not actually stop sophisticated automated traffic; they raise costs marginally for bot operators while significantly degrading the experience for legitimate users — breaking screen readers, accessibility tools, academic crawlers, and archiving services in the process. The HN thread on the essay generated 121 comments, with infrastructure engineers defending bot mitigation as necessary and open-web advocates arguing the collateral damage to non-commercial automated access is already severe.
The cfsolve library's existence arguably supports the essay's thesis: if a motivated developer can defeat Turnstile without a headless browser, the security guarantee is weaker than advertised, but the friction imposed on legitimate users is just as real as ever. Observers noted that the decisions shaping this equilibrium are being made almost entirely by commercial actors — Cloudflare, Google, Akamai — with essentially no democratic input into where the line between protection and openness should fall.
A separate technical piece from bellone.com on double-buffering patterns with Cloudflare Queues illustrated a related point about infrastructure concentration: Cloudflare now occupies a position simultaneously as the platform on which bot detection runs, the platform bots attempt to defeat, and an architecture layer for complex asynchronous workloads. The HN community regularly debates whether that degree of concentration in a single vendor creates systemic fragility that outweighs its conveniences.
AI Rewrites the Stack — and the Entry-Level Career Path With It
A Fortune report that Cisco president Jeetu Patel gave a twenty-seven-year-old engineer unlimited AI tokens to rewrite legacy code drew 205 points and 240 comments — figures that signal the HN community has strong views on what the story actually means. The business case, as the community acknowledged, is straightforward: legacy codebases are expensive to maintain, difficult to staff, and represent compounding technical debt. The ROI of AI-assisted modernization is genuinely compelling for an organization carrying decades-old infrastructure.
But the comments pushed toward a harder question: if AI-augmented senior engineers can now handle the bounded, well-defined tasks that traditionally trained junior engineers, where does the next generation of senior engineers come from? An essay on the same day's feed from ideolalia.com, titled 'Trapped in the Technologist Factory,' argued that the tech industry's pipeline already treats engineers as fungible production units, leaving the field brittle when tools or paradigms shift. The two pieces read together suggest a tension between optimizing for current output and preserving the systemic resilience of the profession itself.
Skeptics in the thread raised a specific risk embedded in legacy rewrites that speed alone cannot address: legacy code frequently encodes decades of business logic, edge-case handling, and regulatory compliance that no one fully understands anymore. A rewrite that produces syntactically modern code may omit behaviors the old system had — including legally binding ones that nobody remembered were there until they broke. If AI acceleration addresses writing speed but leaves knowledge-capture and behavioral validation as the binding constraints, the throughput gain may be more apparent than real. Whether Cisco's rewrite ships cleanly or requires extensive regression remediation over the next year is expected to provide a meaningful data point.
A separate interview with Lean creator Leo de Moura, covering his work at AWS on AI-assisted formal verification, represents a different branch of the same question. Formal verification tools like Lean, Coq, and Isabelle can prove software correct, but have historically required substantial mathematical background to use, making them prohibitively costly for most production contexts. De Moura's argument is that AI can lower the cost of producing those proofs significantly — potentially enabling verified correctness for critical infrastructure code before it ships. The HN thread noted a recursive complication: if AI writes the proof, and AI can be wrong, a further verification layer is required, bottoming out on something humans can check.
NESformers, Wii Macs, and the Love of Constrained Machines
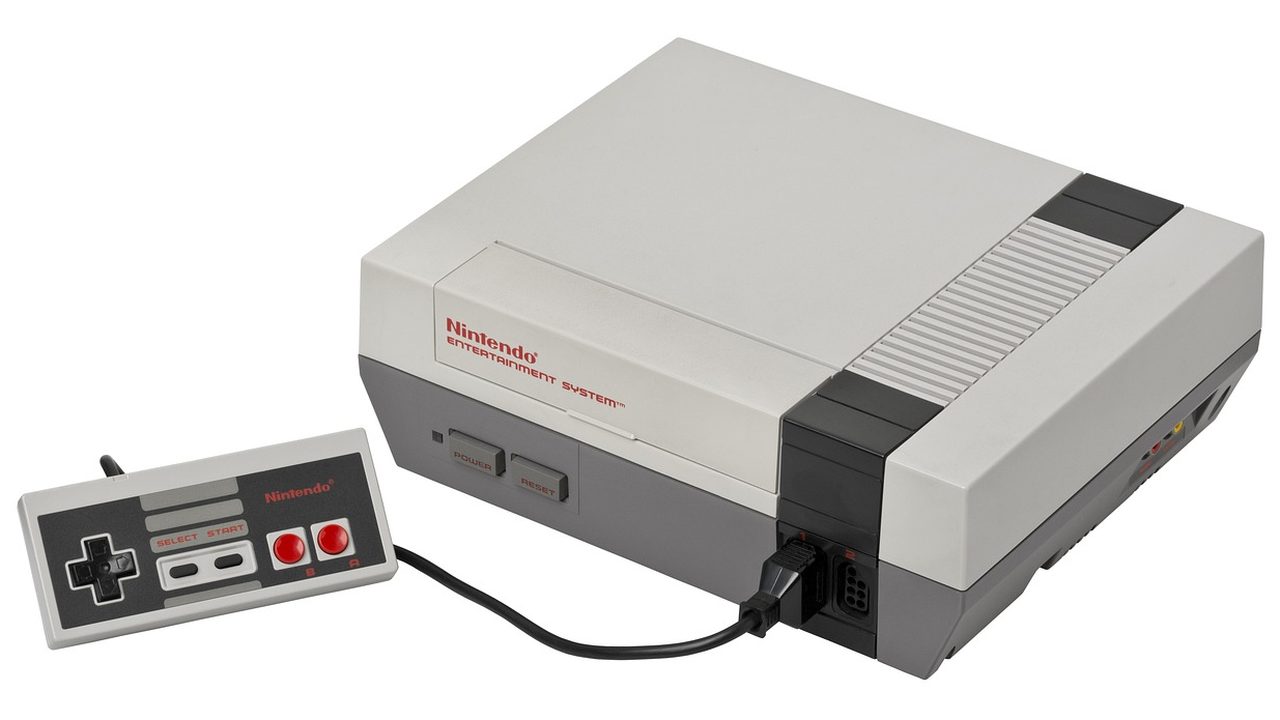
A GitHub project called NESformer — a working Nintendo Entertainment System running inside approximately one gigabyte of Qwen language model weights — gathered 256 points and 122 comments. The project, posted under the handle dbreunig, is not emulation in the conventional sense: the model learned NES behavior from gameplay data well enough to reproduce it from weights alone. The original NES ran at roughly 1.79 megahertz with 64 kilobytes of RAM; encoding a functional approximation of its behavioral space into a gigabyte of transformer weights implies that space is surprisingly compressible in the right representational format, which commenters described as a nontrivial result.
Comments debated whether the system is 'really' running a Nintendo or approximating one — a philosophical question about emulation versus simulation that several threads framed explicitly in Turing Test terms. If the model produces frame-perfect correct output for every game, does the underlying mechanism matter? The question remained productively unresolved.
A piece at virtuallyfun.com titled 'My favourite PowerMac is a Nintendo Wii' drew 314 points and 91 comments for its account of running Mac OS X on Wii hardware through a combination of virtualization layers and the shared PowerPC processor architecture that the Wii and the PowerMac G4/G5 series used. Separately, Infinite Mac added support for BeOS — the mid-nineties operating system that featured per-object threading, a 64-bit journaling filesystem, and real-time audio processing years before those capabilities were standard — making it browsable as a living historical document.
A Show HN from the creator of Marelleo, an open-source story box for children built on an ESP32 microcontroller, captured 78 points and 27 comments. The project at zebra.rodeo emerged because commercial alternatives did not do exactly what the developer wanted; its thorough documentation reflects the maker culture norm of building a thing, then open-sourcing it so others can do the same. A history of DEC's PDP series at entropicthoughts.com rounded out the day's retro computing thread, with the community noting that understanding why Unix and C were designed as they were requires understanding the constraints of the PDP-7 and PDP-11 — context that is explanatory rather than merely nostalgic.
Federated Forges, Rust Protocols, and the Compilers Beneath the Code
Florilegium, a LaTeX-based procedural flower generator on GitHub under the handle kevinraymond, drew 295 points and 47 comments — a remarkable total for generative art built in a typesetting language. The project uses TikZ, a Turing-complete drawing language embedded in LaTeX, to produce mathematically specified floral forms. TikZ experts in the thread noted that the tool can generate graphics with a degree of mathematical precision that would be laborious in any other medium, and that Florilegium treats it seriously as a creative rather than merely technical instrument.
Matching Florilegium exactly at 295 points, with 85 comments, was Tangled — a federated code forge at tangled.org. The concept places git repositories, issues, pull requests, code review threads, CI/CD integrations, and contributor identity on a federated network rather than in a single corporate silo, allowing users to migrate between forge instances without losing history or social graph. Engineers in the thread worked through the protocol design challenges: ActivityPub, which underlies Mastodon, was designed for short social posts, and extending it to code-collaboration semantics requires either significant protocol extensions or a parallel approach. The debate over what minimum viable federation looks like — repositories alone, or the full collaboration layer — continued without resolution.
Firezone's Sanstun project, a sans-IO parallel-friendly WireGuard implementation in Rust, drew 137 points and 28 comments. The sans-IO design pattern separates all protocol logic from actual I/O, producing events and accepting external data while leaving I/O to the caller; the pattern makes implementations significantly easier to test, parallelize, and embed in larger systems with their own async runtimes. WireGuard has been the prevailing modern VPN protocol for several years, and Firezone's implementation is motivated by production needs in enterprise VPN infrastructure rather than pure research.
A deep compiler internals piece from xoranth.net on switch statement lowering in GCC attracted 77 points and 7 comments. The article explains that switch lowering is not a single transformation but a family of strategies selected by the compiler based on the density and range of case values: dense integer ranges become jump tables, sparse ranges may become binary search trees or hash-based dispatch. Understanding which strategy fires and why has concrete implications for performance-critical code paths. A brief note on the Molly Signal fork — reportedly unpatched for three months with known vulnerabilities — attracted only 9 points but was cited as a genuine security concern for users who switched to the fork for its additional features.
Glacier Archaeology, a Lost Verne Novel, and Accountability on the Record
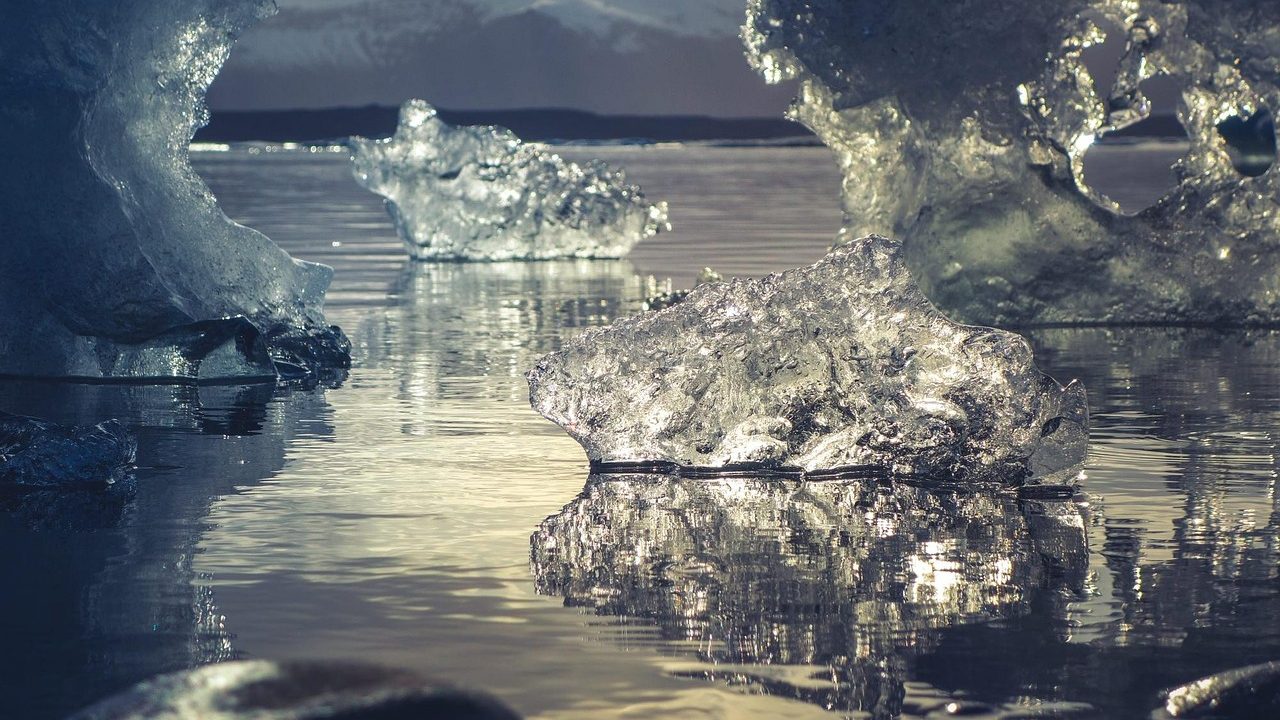
Science Norway's coverage of Stone Age artifacts emerging from melting Norwegian mountain glaciers drew engagement for a reason that goes beyond curiosity: the objects — tools, arrows, preserved fabric — have been held in ice for thousands of years and represent direct material evidence of how people lived in those regions. Once exposed, they begin to degrade unless recovered quickly. The archaeology, as the piece notes, is racing the climate.
A manuscript discovered in Jules Verne's archives and covered at blue-continuum.com — a novel that had never been published — drew 120 points and 28 comments. The piece examines what the work reveals about Verne's views on Paris and urbanism, and whether his vision anticipated anything about how cities actually developed. The HN thread reflected a community that reads Verne seriously as a thinker, not only as an adventure writer. A Star Trek: The Next Generation episode guessing game at tng.episodle.com, submitted as a Halloween tribute to Sir Patrick Stewart, reached 197 points and 55 comments — with threads full of people sharing which episodes stumped them and which plots they felt still hold up.
Serbia's incoming parliament, covered by science.org as potentially the world's most academically credentialed legislative body, drew 91 comments — many focused on the genuinely contested empirical question of whether technical expertise in elected office translates to better governance. Vitalik Buterin published an essay on digital minimalism on Halloween at his personal site, advocating intentional reduction of digital consumption and complexity. The HN community noted the tension of receiving that message from someone whose career is built on a maximally complex digital system, and gave it 73 points and 44 comments.
The episode concluded with two on-the-record corrections. A May episode incorrectly stated that Ukraine had struck a Russian ship in the Caspian Sea — a claim that is geographically impossible, as the Caspian is landlocked and far from Ukrainian-controlled territory, and one that no credible reporting supported. The same episode made a forward-looking claim — that companies ignoring a particular trend would face unexpected competition — framed with false precision despite being unfalsifiable. Both errors were acknowledged without qualification.