From Cracked CA Keys to Climate Targets: A Day of Trust Infrastructure Under Stress
A certificate authority trusted by every major browser was found running cryptographic keys so weak a researcher cracked them in milliseconds, headlining a day in which the foundational trust systems of the web, the cybersecurity industry, AI products, and international climate commitments all came under scrutiny simultaneously.
How this was made Verified AI
Every Intellegix briefing is generated from that day's broadcast and run through automated checks before it publishes — with a human paged on any flag. Here is the trail for this edition.
The Day the Padlock Lied: Inside a Certificate Authority Crisis
The story generating more than 400 Hacker News comments begins with a number: eight. That is the bit-length of RSA keys discovered in an intermediate certificate chain operated by eMudhra, an Indian certificate authority holding trusted root status in major browser stores worldwide. Modern RSA certificates use 2,048 to 4,096-bit keys. Eight bits is not a rounding error or a misconfiguration — it is a key so trivially weak that UK security researcher Scott Helme was able to factor it, meaning crack it entirely, in milliseconds.
The practical stakes are severe. When a browser displays the padlock icon indicating a secure connection, it is vouching for a chain of certificates anchored at a root CA the browser has explicitly decided to trust. If an intermediate CA's keys are compromised, an attacker could in principle generate certificates for any domain that would appear fully valid — enabling man-in-the-middle attacks in which a browser would truthfully report a fraudulent certificate chain as legitimate. A dedicated disclosure site, emudhra.we-have-a-problem.com, documents the responsible disclosure timeline and eMudhra's response.
The Hacker News community is split between outrage directed at eMudhra and deeper structural questions about the web's public key infrastructure. The entire system depends on browsers maintaining a list of trusted organizations; negligence or compromise at any one of them cascades through the whole. A key question the thread has not yet cleanly answered: how an eight-bit key — almost certainly a test or dummy credential never intended for live use — entered a certificate chain that browsers accept as authoritative.
The Negotiator Was the Extortionist: ShinyHunters and the Limits of Cyber Consulting
Federal investigators reportedly suspect that a professional ransom negotiator — hired by victim companies to manage extortion demands from the ShinyHunters hacking group — was himself operating or affiliated with the ShinyHunters infrastructure, according to a report by Brian Krebs at KrebsOnSecurity. ShinyHunters is responsible for some of the largest data breaches in recent years, including incidents affecting Ticketmaster and Santander, with a playbook of exfiltrating datasets and threatening publication unless companies pay.
The business of ransom negotiation has always carried implicit ethical ambiguity. Specialized firms command premium fees partly on the basis of knowing how to talk to ransomware actors — having, as the industry frames it, backchannel access and established relationships. If the federal allegations hold up, they offer a concrete and damning explanation for at least one firm's effectiveness: the negotiator's insight derived from a conflict of interest that is also a federal crime.
The Hacker News thread is wrestling with the systemic implication. The ransom negotiation industry operates without a licensing body, regulatory oversight, or meaningful transparency requirements. SEC disclosure rules for material cybersecurity incidents have driven more companies toward professional negotiators, expanding the market for services that remain almost entirely unverified. Whether this case represents an isolated bad actor or points to a broader structural problem in the ecosystem is a question the comments have not resolved.
Meta's Muse Exposes Private Conversations, PHP Braces for Critical Patch
Ars Technica is reporting that Meta's Muse product — actively marketed as a business productivity AI tool — contains a data isolation failure: sharing a conversation via link reportedly exposes not only the intended exchange but metadata and in some cases content from adjacent sessions, including business strategy discussions and personal information. The Hacker News thread, with 94 comments and a score of 202, reflects genuine alarm from developers who note that AI conversation platforms are routinely handling proprietary code, business plans, medical questions, and legal matters — data whose sensitivity demands security engineering that the Muse evidence suggests is absent.
Separately, the PHP security team issued a pre-announcement for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, flagging an upcoming emergency release before the patch is publicly available. The approach is designed to give major hosting providers and distribution maintainers time to prepare rapid deployments. PHP still powers an enormous share of the web — WordPress alone accounts for roughly 40 percent of all websites globally — meaning a critical remote code execution vulnerability in PHP's core would rank among the most broadly exploitable issues in web security. The Hacker News comments are populated with sysadmins and hosting providers coordinating patch timelines, a mood of organized urgency that suggests the pre-announcement strategy is functioning as intended.
DeepSeek's Inference Engine Electrifies Developers; Mistral Enters the Voice Race
DeepInfer, DeepSeek's open-source high-performance inference framework, landed as the highest-energy release on Hacker News on Wednesday, accumulating over 2,200 points and 862 comments. The framework is optimized specifically for DeepSeek's own model architecture and claims substantially better throughput and latency than generic inference stacks such as vLLM and TGI when running DeepSeek models. The comment thread has become a live community benchmarking session, with engineers posting A100 and H100 throughput numbers across different batch sizes and memory configurations — a format Hacker News is particularly suited to for infrastructure releases.
The strategic logic mirrors moves by other large model providers: releasing a first-party inference framework removes optimization friction and creates an adoption incentive that is open-source in license but creates a performance moat around the model creator's own architecture. Mistral's simultaneously released Voxtral 3 pursues a different vector — a voice AI model that processes audio natively rather than transcribing to text before inference, preserving tonal and acoustic context that transcription loses. Mistral is positioning the model for voice agent applications, and its 697 points and 172 comments reflect genuine developer interest in a segment of the open-weight model space that remains thinner than the text model market. Early latency numbers in the thread are reportedly competitive, though commenters note that production deployment context matters enormously for real-world performance.
Benchmarks, Slop, and the Limits of Context Engineering
The October 2026 SlopCodeBench results compare leading AI coding models on tasks specifically designed to elicit 'slop' — code that appears plausible but contains subtle quality failures. Astra wins the overall ranking; Opus 5.5 is competitive but not the top performer. The most counterintuitive finding is that the 'xhigh' context engineering approach — providing models with highly elaborate instructions — is flagged as actively harmful to output quality. The hypothesis is that models overoptimize for the complexity of the instruction set and produce code that is technically responsive to the prompt but practically worse than what simpler prompting achieves.
Hacker News commenters are interrogating what the benchmark actually measures. The xhigh finding may be specific to SlopCodeBench's task distribution rather than a universal principle about model behavior under rich context. If teams running Opus 5.5 with sophisticated context engineering in production report substantially better outcomes than the benchmark implies, or if Astra's lead does not translate to practitioner preference in real-world comparisons, those would be signals that the benchmark is miscalibrated. The broader caution applies to DeepInfer's early community benchmarks as well: engineers who post results are more likely to post when results are interesting or positive, introducing selection bias even in independent testing.
CSS Gets Serious, C# Challenges Rust, and Google Opens Its TPU Stack
Josh Comeau's piece on the Interop 2027 initiative is generating front-end developer enthusiasm for a concrete reason: browser vendors including Chrome, Firefox, and Safari are committing to consistent implementations of several long-awaited CSS capabilities, including masonry layout, anchor positioning, cross-navigation view transitions, and improved color space support. CSS anchor positioning — which would allow UI elements like tooltips and dropdowns to be positioned relative to other elements declaratively, without JavaScript — is drawing the most HN excitement, with multiple developers saying it would let them remove entire JavaScript dependencies from their projects. Interop programs have measurably accelerated practical adoption of web standards by eliminating the polyfill burden that browser inconsistency imposes.
The NetWasm project presents a finding that surprises most practitioners: C# compiled to WebAssembly can produce smaller binaries than equivalent Rust in certain configurations, challenging the assumption that Rust is the ideal WASM compilation target. Microsoft's investment in Blazor and the .NET WASM story is showing up in measurable output, though HN commenters note that binary size is one metric among several — startup time, runtime performance, and memory footprint remain equally important depending on use case. Google's simultaneous open-sourcing of TorchTPU, a native PyTorch backend for its Tensor Processing Units, represents a parallel effort to lower switching costs from NVIDIA's CUDA-dominant ecosystem. The prior XLA compiler path for TPU-PyTorch interop carried ergonomic friction; TorchTPU presents as a native backend requiring substantially less code modification, earning 349 points on HN.
HyperCard's Ghost, a Quantum Basement, and a Tank Game in the Browser
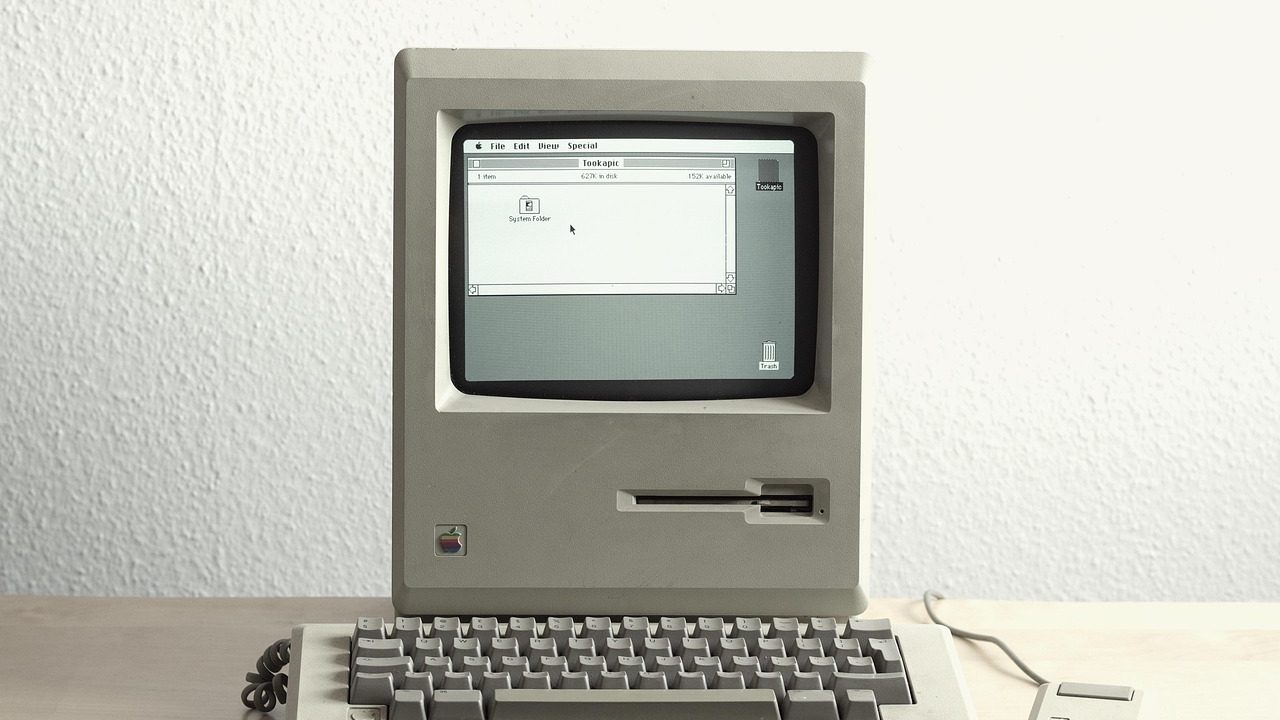
A four-year retrospective on Decker — a HyperCard-inspired creative computing environment — captures the appeal of tools that prioritize expressiveness over raw capability. HyperCard, Apple's 1987 tool that gave non-programmers access to interactive multimedia authoring, was discontinued in 2004; Decker is described as the most serious modern attempt to recapture that design philosophy. At the opposite end of the complexity spectrum, a Show HN entry for Linkit, a 100-percent free and open-source AI-powered bookmark manager, illustrates the growing category of personal information management tools built around LLM-powered organization — with the persistent open question of whether AI categorization reduces retrieval friction or replaces transparent tagging with opaque inference.
Quanta Magazine's piece on Hilbert space and quantum computational complexity is drawing clarification from HN commenters working in quantum computing, who are distinguishing between mathematical results about what quantum systems could do in principle and what near-term noisy intermediate-scale quantum devices can actually accomplish. The BZFlag Online project — which ports the 1990s open-source tank game to run in a browser via WebAssembly — and the Dorchester 3D-printed case that converts a ZX Spectrum Next into a laptop form factor both reflect a broader HN interest in retrocomputing preservation and the cultural memory of early home computing, particularly among British programmers for whom the original Spectrum represents a formative platform.