Crypto Heist, AI Backdoors, and the Death of a Cultural Icon: Hacker News Captures a Turbulent Friday
A reported $5.6 billion theft from Binance, a supply chain attack targeting AI developer tools, and the death of Patrick Stewart collided on Hacker News on October 30, 2026 — a single day that exposed fault lines running through crypto infrastructure, AI security, and the culture of the people who build the internet.
“At scale, you're not fighting hackers, you're fighting the complexity of your own system.”
How this was made Verified AI
Every Intellegix briefing is generated from that day's broadcast and run through automated checks before it publishes — with a human paged on any flag. Here is the trail for this edition.
A Generation Mourns the Captain Who Made the Future Worth Reaching
Patrick Stewart died at 86, and the Hacker News community responded with more than 3,000 points and nearly 650 comments — a volume that reflects just how foundational Star Trek: The Next Generation has been to engineering culture. The thread is not a simple condolence board. It is a community working through something genuinely meaningful.
Commenters parsed specific episodes, debated the Prime Directive as an early articulation of something like the precautionary principle in technology deployment, and examined Captain Picard as a model of leadership that prized intellect and principle over hierarchy. Stewart came out of the Royal Shakespeare Company and initially approached the Picard role with some skepticism; the moral seriousness he brought to it aged remarkably well relative to most science fiction of that era.
His second major pop-culture anchor — Professor Xavier in the X-Men films — carried its own resonance for the tech world. The role explored minority identity, the relationship between power and responsibility, and what institutions owe to people who fall outside their default assumptions. Those themes have run through painful, ongoing conversations in the industry.
The HN thread also quoted a line from TNG's series finale — 'I sincerely hope that will be not the last time' — and noted how differently it reads today. Stewart was reportedly working on stage projects as recently as last year. The community's reaction stands as a primary document about what a forum simultaneously debating crypto exploits and video compression actually values: the people building toward the future paused to mark the loss of someone who made that future feel worth reaching.
The Largest Centralized Exchange Heist on Record — If the Numbers Hold
The figure attached to the reported Binance hack of October 29, 2026 is $5.6 billion. For context, the 2022 Ronin Network exploit — attributed at the time to North Korea's Lazarus Group — amounted to approximately $625 million. The Mt. Gox collapse in 2014 involved around 850,000 bitcoin, valued at the time at roughly $450 million. If the figures from Arkham Intelligence's on-chain tracker hold, this would represent the single largest theft from a centralized exchange on record.
The Hacker News thread, which drew nearly 940 comments, features blockchain analysts, former exchange employees, and users who are understandably furious. The technical discussion centers on how the attack was structured: the pattern of fund movements suggests multiple withdrawal paths, layered obfuscation through mixing protocols, and a pre-planned exit route across several chains — not a simple hot wallet compromise.
A recurring theory in the thread holds that Binance's compliance-driven restructuring may have inadvertently created new attack surfaces. Regulatory requirements around access logging, audit trails, and multi-signature wallet architecture can conflict with security best practices; changes made to satisfy regulators may have altered internal access controls in ways that opened privilege escalation paths. One commenter with apparent exchange security experience put it concisely: 'At scale, you're not fighting hackers, you're fighting the complexity of your own system.'
Binance has not confirmed the full scope of the breach. Some portion of the funds could theoretically be recovered — the Poly Network hacker returned the entirety of a $611 million exploit in 2021 — but given the scale here, the incentive to do so appears unlikely. The reputational damage arrives at a particularly fraught moment: Binance's founder Changpeng Zhao stepped back from the CEO role in late 2023 as part of a DOJ settlement, and current leadership has been navigating a post-enforcement posture. Firms including Arkham, Chainalysis, and Elliptic are reportedly working to trace the funds, and whether the pattern points to a nation-state actor or a sophisticated criminal organization may become clearer as that analysis matures.
The exploit renews a structural debate about centralized versus decentralized custody. Centralized exchanges remain the primary on-ramp for most retail crypto participants, but their custodial model means users are trusting someone else's security posture with their assets. Decentralized alternatives carry their own catastrophic exploit history. The tension between user-experience advantages and custodial risk has no clean resolution, and events of this magnitude have a way of forcing that conversation back to the surface.
Mistral Opens the Frontier — While Anthropic's Developer Tools Are Reportedly Compromised
The AI news this week pulled hard in two directions. Mistral released the weights for Mistral Large 4 as open-source — drawing more than 1,500 points and 400 comments on Hacker News — while simultaneously a pair of security stories emerged about backdoored Claude Code extensions and what appears to be a breach of Anthropic's own infrastructure used to deliver a remote access trojan to developer laptops.
Mistral Large 4 reportedly benchmarks competitively with models not being released as open-source, in a range described as GPT-4 class or potentially higher on certain tasks. Open-sourcing the weights means any developer can run the model on their own infrastructure, fine-tune it on proprietary data, and deploy it without API costs or terms-of-service constraints. From a competitive strategy standpoint, the move follows Mistral's pattern of aggressive open-source releases: the French company is well-funded but not at the scale of Anthropic or OpenAI, and building ecosystem through open weights may generate infrastructure leverage even without direct API revenue.
The release lands alongside a sharp critique of how model quality is actually measured. A piece from the Interconnects newsletter, linked in the HN thread, describes what it calls the benchmarker's dilemma: the moment a benchmark becomes widely associated with model quality, training labs — whether deliberately or through data contamination — begin optimizing toward it, so scores rise while real-world capability improvements may be much smaller. Artificial Analysis v5 is attempting a dynamic benchmark approach, refreshing test cases regularly to prevent pre-training; HN commenters note that even dynamic benchmarks carry structural biases favoring certain architectures. Enterprise buyers making procurement decisions based on published rankings are, in effect, purchasing optimized test scores.
Martin Fowler's essay on LLM voice interfaces attracted 496 points and 262 comments, exploring whether talking to an AI rather than typing represents a fundamental shift in interaction paradigm or primarily a convenience layer. The practical developer question — whether spoken queries, which tend to be more conversational and less precisely specified than typed ones, are handled gracefully by current models — remains empirically unsettled.
The security stories are more immediately alarming. Kevin Beaumont's doublepulsar.com blog — described in the HN thread as a highly credible security research source — reports a supply chain attack through Claude Code's extension ecosystem in which developers who installed what appeared to be legitimate extensions may have received malware granting remote access to their machines. A related post describes what appears to be a compromise of Anthropic's own development infrastructure. Both stories were breaking as of this morning and carry only a small number of HN comments, suggesting they surfaced recently; Anthropic had not publicly confirmed the full scope. Developers using Claude Code extensions were advised in the thread to audit their installed extensions and review network activity on development machines immediately. The broader structural issue, as the HN community noted during npm ecosystem attacks in previous years, is that developers necessarily install and run large amounts of third-party code — and the security model that says 'trust packages from official sources' breaks the moment official sources are compromised.
From H.264 to Hyperbolic Space: The Nerd Joy That Makes Hacker News Worth Reading
A 2016 article titled 'H.264 Is Magic' is sitting at 450 points on Hacker News in 2026, and the fact that a decade-old technical explainer generates that engagement is its own argument for the piece's quality. Author Sid Bala walks through the core techniques behind the codec: spatial redundancy within frames handled through discrete cosine transforms, temporal redundancy across frames via motion estimation, and psychovisual tricks that exploit known limitations of human perception to discard information viewers cannot detect. H.264 remains the most widely deployed video codec in the world, embedded in essentially every camera, streaming service, video conferencing platform, and display device — understanding how it works is genuinely useful for any developer touching video. The thread also debates whether AV1 or H.266's successors will displace H.264 at the consumer hardware level within the next decade; the emerging consensus is probably not fully, because the installed base of H.264 hardware decoders creates inertia that makes replacement economically painful.
Astroterm, a terminal-based planetarium that renders the night sky in a command line, is drawing 155 points and enthusiastic comments. It is the kind of project that thrives on HN: technically elegant, impractical in the best sense, and beautifully executed. The comments fill with requests for ISS tracking, satellite passes, and deep sky objects; the project appears to be actively maintained on GitHub.
An interactive piece reimagining IPv4 address space as physical land ownership is generating over 410 comments — among the highest engagement counts of the day. The visualization reveals extreme concentration: the U.S. Department of Defense holds address blocks that would constitute a small continent; early academic institutions hold ranges equivalent to major nations; the global south received almost nothing in the original allocation. This matters concretely because IPv4 addresses now trade on secondary markets at roughly $50 to $60 per address. Microsoft paid approximately $11.25 per address for Nortel's blocks in 2011; the same addresses would fetch around five times that today. The thread's deep dive into why IPv6 adoption has stalled for approximately twenty-five years settles on a practical explanation: carrier-grade NAT has allowed existing IPv4 space to stretch far beyond early projections, removing the pain that would otherwise force a transition.
Cuis Smalltalk is drawing attention from a community with genuine affection for Smalltalk as an underappreciated lineage in programming language design. Cuis positions itself as a modern, minimal implementation of Smalltalk-80 — the 1980 version that influenced Objective-C, Python, and Ruby. Several commenters use it for education and note that Smalltalk's image-based development model, in which entire program state persists and remains introspectable live, is something modern environments still have not fully replicated. And then there is the billiards-in-hyperbolic-space video, at 151 points, where balls on a surface with negative curvature violate the reflection rules of flat Euclidean geometry in ways that are visually disorienting and beautiful — the kind of mathematical recreation content, educational and unmonetized, that HN surfaces exceptionally well. Finally, Pico CSS announcing it is no longer maintained attracted 153 points and a thoughtful discussion: the maintainer cited years of open-source work without sustainable funding, and the community's response has been respectful of that reality rather than simply asking for alternatives.
Black Holes, Game-Playing Agents, and Why the Open-Source AI Consensus Deserves Scrutiny
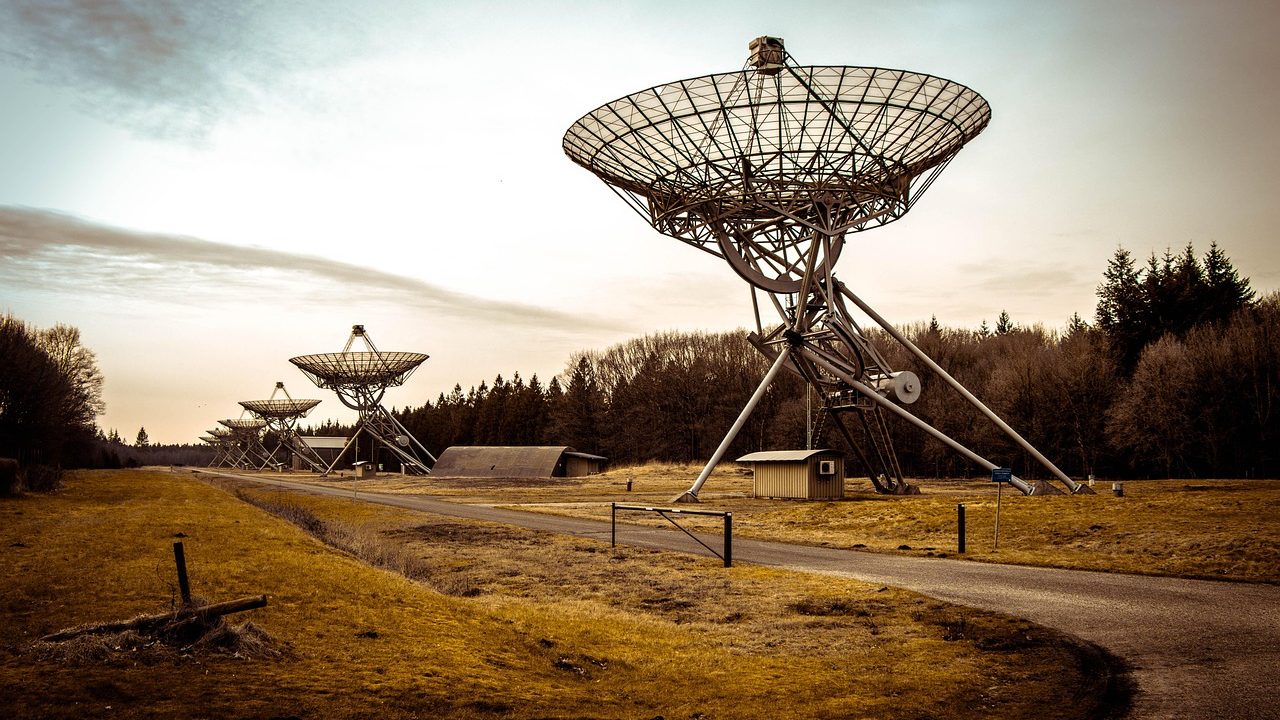
A Quanta Magazine piece on black hole imaging is prompting discussion of the methodology behind the Event Horizon Telescope collaboration — the project that produced the 2019 image of M87's shadow by synchronizing radio telescopes across multiple continents into a virtual dish the diameter of Earth, requiring timing precision in the picosecond range. The current work described in the article pushes toward near-real-time imaging, which would allow researchers to observe dynamics in the accretion disk rather than a single moment's configuration.
A YC Labs project studying AI agent swarms in Minecraft and Mindustry drew 306 points and 113 comments. The researchers use open-world games as controlled environments for multi-agent coordination: Minecraft for open-ended building and survival requiring resource management and complex construction, Mindustry for supply chain optimization under time pressure. HN commenters who read the technical writeup report that agents show emergent division of labor — some specializing in resource gathering, others in defense or construction — that was not explicitly programmed. Whether this constitutes genuine coordination or sophisticated pattern-matching remains contested; the researchers themselves reportedly characterize the answer as uncertain, which commenters treat as the intellectually honest position.
Other notable technical projects: Simantic, a YC F26 startup, is building firmware simulation for AI agents — infrastructure aimed at closing the sim-to-real gap that represents a major bottleneck in embedded AI deployment. The tinyworldformer project runs a small transformer modeling game states on a Raspberry Pi Pico 2 W, which has 264 kilobytes of RAM; that transformer inference is possible at all on microcontroller-class hardware is described in the thread as remarkable. The DoomFormer project on GitHub trains models to predict DOOM game states frame-by-frame, learning the physics of the environment through observation — a domain useful for research because ground truth is known exactly.
The episode's most substantive analytical moment involves stress-testing the community consensus around Mistral Large 4's open-source release. HN broadly treats open-sourcing frontier-class models as unambiguously beneficial — democratizing access, enabling innovation, reducing vendor lock-in. The counterargument is that releasing weights is a one-way door, and the risk profile of frontier-class models differs meaningfully from earlier open-source releases. The concern centers not on content policy violations but on capability thresholds for harm becoming globally available to actors with no interest in safety guidelines. However, for that argument to hold, one must believe the marginal risk added by open release is significant — that sophisticated state actors couldn't achieve comparable capabilities through other means — which is contestable given that nation-states with serious AI programs likely have comparable internal capabilities already.
A further assumption worth examining: the open-source safety argument presupposes that raw capability scaling is the primary risk driver. If the next category of harm instead emerges from fine-tuning or prompting techniques applied to smaller models already in the wild, the frontier open-source debate may be misdirected entirely. The honest position, as framed in the discussion, is that the release constitutes an experiment — and the appropriate response is to watch carefully for documented misuse cases specifically traceable to Mistral Large 4 over the coming months, rather than assuming the answer in either direction. The EU AI Act's provisions for high-capability open-source models add a regulatory dimension that may ultimately constrain the decision space regardless of technical arguments. One additional caveat: the assumption that open-source produces better safety outcomes through community scrutiny has not been tested at this capability level. More eyes on weights does not obviously translate to better safety in the way that more eyes on code translates to finding vulnerabilities.
Trust, Infrastructure, and an Honest Accounting of What We Got Wrong
The through-line connecting Friday's disparate stories is trust and infrastructure. The Binance hack is a trust failure in centralized crypto infrastructure. The reported Anthropic extension backdoors are a trust failure in AI developer tooling. The IPv4 land visualization is ultimately about who inherited the infrastructure of the early internet and what that inheritance means for global access. Mistral Large 4 represents a bet on an alternative trust model — that distributed access to capable models produces a more robust and equitable AI ecosystem than centralized API control. Even Patrick Stewart fits: TNG's vision of the future centered on institutions being trustworthy, on Starfleet as a model of principled bureaucracy, and the outpouring over his death reflects a loss of something that represented a hopeful answer to what institutions could look like.
On the Spain train crash: BBC reporting describes significant casualties and an ongoing investigation into signaling system failure. The HN thread drew 383 comments, reflecting both the human tragedy and substantive technical interest in rail safety systems. That thread is recommended reading for anyone seeking depth on what may have gone wrong and what it implies for infrastructure policy.
Intellectual honesty requires acknowledging errors. In May of this year, a claim was made on this program that Ukraine had struck Russian ships in the Caspian Sea. The Caspian Sea is landlocked, surrounded entirely by Russia, Kazakhstan, Turkmenistan, Azerbaijan, and Iran; Ukraine has no plausible military pathway to conduct naval strikes there. The claim appears to have originated from a dubious source and was repeated without adequate verification. An apology is owed for that error. Additionally, a prediction made in May — roughly that 'companies that ignore this trend will face unexpected competition' — is not a prediction. It is a sentence structured to be technically unfalsifiable. Concrete, falsifiable expectations with specific timeframes are the standard this program will hold itself to going forward.
All of today's stories originated in the Hacker News community at news.ycombinator.com. The podcast uses Claude Code from Anthropic for script generation and production automation, and Perplexity for real-time topic discovery and research — an irony not lost on the hosts given the episode's reporting on Claude Code's extension ecosystem being reportedly compromised, and one they preferred to acknowledge directly rather than paper over.