DeepSeek Opens Its Engine, DHS Slams the Door: A Day of AI Tension, Security Gaps, and the Joy of Building
On a day when DeepSeek open-sourced its production inference engine and the Department of Homeland Security banned the technology from federal networks in the same 48-hour window, Hacker News became the unlikely arena where engineers worked out the ethics, security implications, and simple pleasures of a profession in rapid transformation.
“knowledge already freely available on the internet cannot be sanctioned.”
How this was made Verified AI
Every Intellegix briefing is generated from that day's broadcast and run through automated checks before it publishes — with a human paged on any flag. Here is the trail for this edition.
DeepSeek Opens Its Engine — Washington Moves to Lock the Door
DeepSeek escalated its push into the open-source AI ecosystem this week by releasing DeepInfer, the inference engine the company uses to run its models in production. The release — posted directly to GitHub and available to anyone — is not documentation or a research preview. It is the operational system itself, and early reviewers in the Hacker News community described the code quality as genuinely high.
Within what appears to be the same 48-hour window, the Department of Homeland Security issued an order banning DeepSeek from federal civilian agency IT systems. The Reuters report makes clear the action was a DHS order rather than a congressional statute, meaning it was implemented through executive authority without going through the full legislative process — a distinction that signals how urgently the administration views the threat.
The Hacker News thread on the ban drew 258 comments and repeatedly circled a core tension: if the model weights and the inference engine are already publicly available, what does a federal ban accomplish? The answer, as several commenters worked out, depends on which threat you are trying to address. Federal agencies using DeepSeek's hosted services would be routing potentially sensitive government queries to servers DeepSeek controls — a data exfiltration concern made concrete by China's 2017 National Intelligence Law, which allows the government to compel data from Chinese technology companies. Running DeepSeek's open-source weights on an air-gapped federal system is a categorically different threat model, one centered on whether backdoors or vulnerabilities might be embedded in the model itself.
The strategic logic behind releasing DeepInfer at all is itself contested. One theory circulating in the thread holds that this is ecosystem-building disguised as open-source generosity: if DeepInfer becomes the standard inference runtime that developers build tooling around, DeepSeek's models become the default in that ecosystem by distribution rather than mandate. The geopolitical reading runs alongside it — open-source releases are one of the few vectors through which Chinese AI development can build credibility and adoption in Western markets that are increasingly hostile to Chinese-hosted services. Each high-quality release makes the policy conversation harder, because knowledge already freely available on the internet cannot be sanctioned.
Flash Models, Abliterated Dangers, and the Agent Benchmark That Lives in a Video Game
MiniMax M3.1 Flash, from Shanghai-based MiniMax, scored 479 points and 204 comments on Hacker News — numbers that signal serious community attention rather than novelty interest. The model draws comparisons to GPT-4o in the efficiency tier, with competitive benchmark performance at dramatically lower inference costs. Notably, community skepticism was more measured than it might have been months ago; more users downloaded and tested rather than dismissing the numbers outright, a posture shift that several commenters attributed to DeepSeek releases repeatedly validating in independent evaluations.
A blog post explaining speculative decoding — the technique underlying many of the recent inference efficiency gains — surfaced alongside the MiniMax discussion. The approach uses a small draft model to generate several tokens ahead while the larger model verifies or rejects them in parallel. Because verification is parallelized and rejection is cheap, throughput increases substantially without changing the model's output distribution. The analogy several commenters reached for was CPU branch prediction: you make a bet on what comes next and pay a cost only when you are wrong.
The most alarming AI story of the day came from ProjectDiscovery, whose research showed that 'abliterated' models — those with safety training removed — are substantially more vulnerable to prompt injection attacks than standard models. The finding is operationally significant for anyone running AI agents that process external content: an attacker who can embed instructions in an email, webpage, or document that an abliterated model reads in an agentic pipeline can hijack the model's behavior. The 85-comment HN thread converged on a working hypothesis that safety training does incidental work teaching models to recognize manipulative instructions, and that removing safety training removes that recognition capacity alongside the content restrictions. Whether this coupling is a fundamental architectural property or an artifact of current training methodology remains an open question — no published paper has yet demonstrated a model that resists prompt injection while failing standard content refusal tests.
On the agent capability frontier, a video benchmarking AI agents in RuneScape — an actively played massively multiplayer online game — drew 204 points and enthusiastic discussion. The argument for MMOs as evaluation environments is that they require long-horizon planning, resource management, navigation, and interaction across hundreds of sequential decisions: exactly the capability gap that makes current agent systems struggle in ways that single-question benchmarks do not reveal. Maxwell, a model positioned between software specification and hardware synthesis, also surfaced with 84 points; the company claims it can take high-level descriptions and produce outputs meaningful to hardware compilers, a capability the semiconductor industry is watching as custom silicon becomes a larger share of AI infrastructure.
OpenBSD 8.0 Brings Modern GPUs and Windows Apps to the Security-Obsessed OS
OpenBSD 8.0 arrived this week to strong community reception — 325 points on its own — but the story that generated the most enthusiasm on Hacker News today, scoring 575 points and 195 comments, was the announcement that Wine has been ported to the platform. That comment total makes it the highest-scoring story on the day's list.
The 8.0 release itself closes a longstanding practical gap by shipping updated graphics drivers sourced from Linux 6.18, including the Intel, Radeon, and AMD GPU driver stacks. OpenBSD's historically conservative approach to hardware support has been one of the primary barriers to using it as a daily driver; modern GPU acceleration for display and compute workloads has lagged significantly behind Linux. The Linux 6.18 driver inclusion substantially narrows that deficit.
The Wine port is the more technically dramatic achievement. Wine allows Windows applications to run on Unix-like systems without a Windows license or virtual machine, but getting it to function on OpenBSD required working against the operating system's own security architecture. OpenBSD enforces a W^X policy — memory can be writable or executable, but never both simultaneously — which is precisely what Wine's JIT compilation approach wants to violate. Contributors to the port worked around that constraint without abandoning the policy, a feat that HN commenters with Wine experience on Linux described as considerably harder than it sounds. The result broadens OpenBSD's potential user base from its traditional home in network appliances and high-security servers toward workstations.
Two other security-adjacent stories rounded out the segment. Go is rejecting certificate chains that include eight specific distrusted Subject Public Key Infos — cryptographic identifiers for certificate authority keys that have been compromised or fallen below modern standards. Because Go maintains its own certificate trust store rather than delegating entirely to the operating system, the enforcement is universal across Go-based infrastructure regardless of what the underlying OS allows. Separately, MicroG — a free and open-source reimplementation of Google Mobile Services — continued gaining attention as awareness grows of how much proprietary Google software sits atop the nominally open-source Android base; the project allows de-Googled Android installations to run apps that technically require Google Play Services by intercepting and handling those API calls through open-source implementations.
The Profession Debates Itself: Joy, AI-Written Code, and the Art of the Monospace Font
The highest-comment story on Hacker News today was not about artificial intelligence, operating systems, or security. It was a blog post titled 'It's Still OK to Enjoy Programming,' by Chris Kiehl, which drew 622 points and 537 comments. The post argues that programming remains intrinsically interesting and worth pursuing for its own sake, independent of automation anxiety, employer valuation, or hype cycles. The scale of the response suggested many readers needed to hear someone say so plainly.
Running simultaneously — and generating 481 points and 614 comments, the highest comment count of any story today — was an Ask HN thread posing a question with genuine professional stakes: what are an engineer's obligations when they ship AI-written code they cannot fully explain? Responses spanned a wide spectrum. Pragmatists argued that shipping code you haven't traced line-by-line is how software has always worked at scale; you don't understand every line of every library you depend on. Others drew a harder line, arguing there is a meaningful difference between depending on tested, documented, human-written libraries with an accountability chain and shipping generated code that was verified only casually. The thread surfaced a useful distinction: not understanding code that is abstracted behind a well-specified interface is how large systems are built; not understanding code because you generated it without constructing a mental model is a new epistemic situation the profession does not yet have established norms for.
Nordwand Mono, a new monospace typeface, earned 311 points and 95 comments — exceptional numbers for a font release. The name references the Nordwand, the north face of the Eiger in the Swiss Alps. The design drew comparisons to JetBrains Mono, Iosevka, and Berkeley Mono, and the discussion about what makes a monospace typeface readable over extended coding sessions was, by community consensus, substantive rather than merely aesthetic.
Two more playful projects captured significant attention. A video documenting the construction of a single-motor drone — challenging the conventional assumption that stable flight requires at minimum three or four motors — earned 562 points and 129 comments, with aerospace-trained commenters turning the thread into an informal seminar on rotary-wing flight dynamics and passive attitude control. Weball, a tool that lets users roll webpage elements into a growing ball in the style of the video game Katamari Damacy, drew 228 points as an illustration of real-time DOM manipulation — and, as several commenters noted, as a demonstration that programming can still produce things that are simply joyful. A separate project cataloging the 88-by-31-pixel hyperlink badges of the late 1990s web, processed using ImageMagick, served as both a technical walkthrough and an act of internet archaeology that prompted waves of recognition in the comments.
When One Cloud Falls: Revolut, HSBC, Lloyds, and the Systemic Risk Nobody Fixed
The Revolut outage reported by the BBC carried a buried lead. Revolut serves approximately 45 million customers across Europe, making its app going down a significant story on its own. But a Neowin report that also surfaced on Hacker News revealed the outage was tied to a Google Cloud incident that simultaneously took down HSBC, Bank of Scotland, Lloyds, and Equifax. That is a different story: a single infrastructure provider failure knocking multiple major financial institutions offline in the same incident.
The scenario is precisely what regulators have been trying to prevent. The UK's Financial Conduct Authority and the EU's Digital Operational Resilience Act — DORA — both contain provisions specifically targeting third-party technology concentration risk in financial services. An outage simultaneously affecting Revolut, HSBC, Lloyds, and Equifax from a single point of failure tests those frameworks against reality.
Research from IPInfo surfaced a related infrastructure exposure in a different sector: commercial refrigeration systems across French supermarket chains were reportedly accessible via the public internet with no authentication — direct IP access — for what appears to have been months. The security implications run on multiple axes. Temperature manipulation could compromise food safety without triggering immediate alerts. At scale, coordinated manipulation of commercial refrigeration systems also represents a potential demand-side grid attack vector, since commercial refrigeration accounts for a significant portion of retail electricity consumption. The 161-comment HN thread attributed the pattern to a recurring problem in operational technology security: network connectivity was retrofitted onto industrial systems designed before cybersecurity was a primary engineering concern, and the responsible network segment lacked access controls.
A smaller but pointed supply chain story: the real XScreenSaver project maintains no official GitHub repository — its author, Jamie Zawinski, does not maintain one. A repository named 'xscreensaver-official' appeared on GitHub and was superficially convincing. The HN post flagging the impersonation noted that legitimate maintainers generally do not append 'official' to their repository names; that is a pattern associated with counterfeit accounts establishing credibility. The recommended verification path is the project's actual website or documentation rather than GitHub search results.
A Drone Carries a Soldier Home — and a Show Corrects the Record
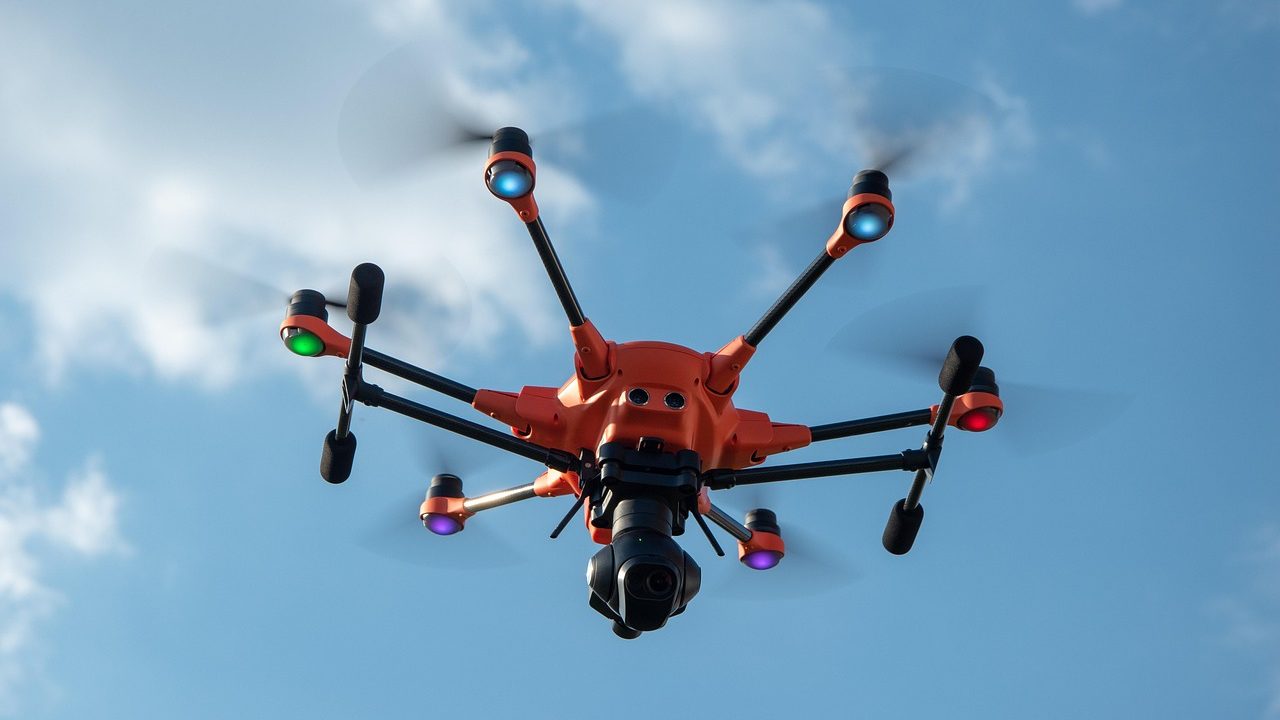
Ukraine reportedly carried out the first documented drone evacuation of a wounded soldier from a front-line position, using a hexacopter with a stretcher attached to the aircraft. The story drew 310 points and 241 comments on Hacker News. The hexacopter used was a commercial platform adapted for the purpose — consistent with how drone innovation in the conflict has broadly proceeded, with off-the-shelf commercial hardware being adapted for military use faster than any formal procurement cycle could match.
The HN thread divided between readers focused on the humanitarian dimension — drones reducing the exposure of medics who would otherwise have to cross contested ground — and those thinking through the military technology implications. The through-line connecting the drone evacuation to other stories on the day's list, from the single-motor drone video to the RuneScape agent benchmarks, is that the frontier of what autonomous systems can do is being explored through improvisation as much as through formal development programs.
The hosts of the podcast closed with an unusual act of public correction. In an episode from May 18th, they stated that Ukraine had struck Russian ships in the Caspian Sea — a claim they said lacked any credible evidentiary basis and was geographically implausible given known distances and strike capabilities. 'We got that wrong, and we're saying so plainly,' the hosts acknowledged. The same episode made a vague prediction about companies facing unexpected competition — a formulation they described as its own failure, since a prediction that can be confirmed by almost anything is not a real prediction. The hosts said they are working toward more specific and verifiable forward-looking claims and committed to flagging when they fall short of that standard.